Contents
- Introduction
- The seven notices at a glance
- After the 12:00 deadline (10th and 11th notices)
- The attacker’s site taken down (13th notice)
- Device analysis (14th notice)
- Special payment and bounty (12th notice)
- Toward identifying the culprit (15th notice)
- What news reports say
- What users should do
- The entry route may stay unconfirmed
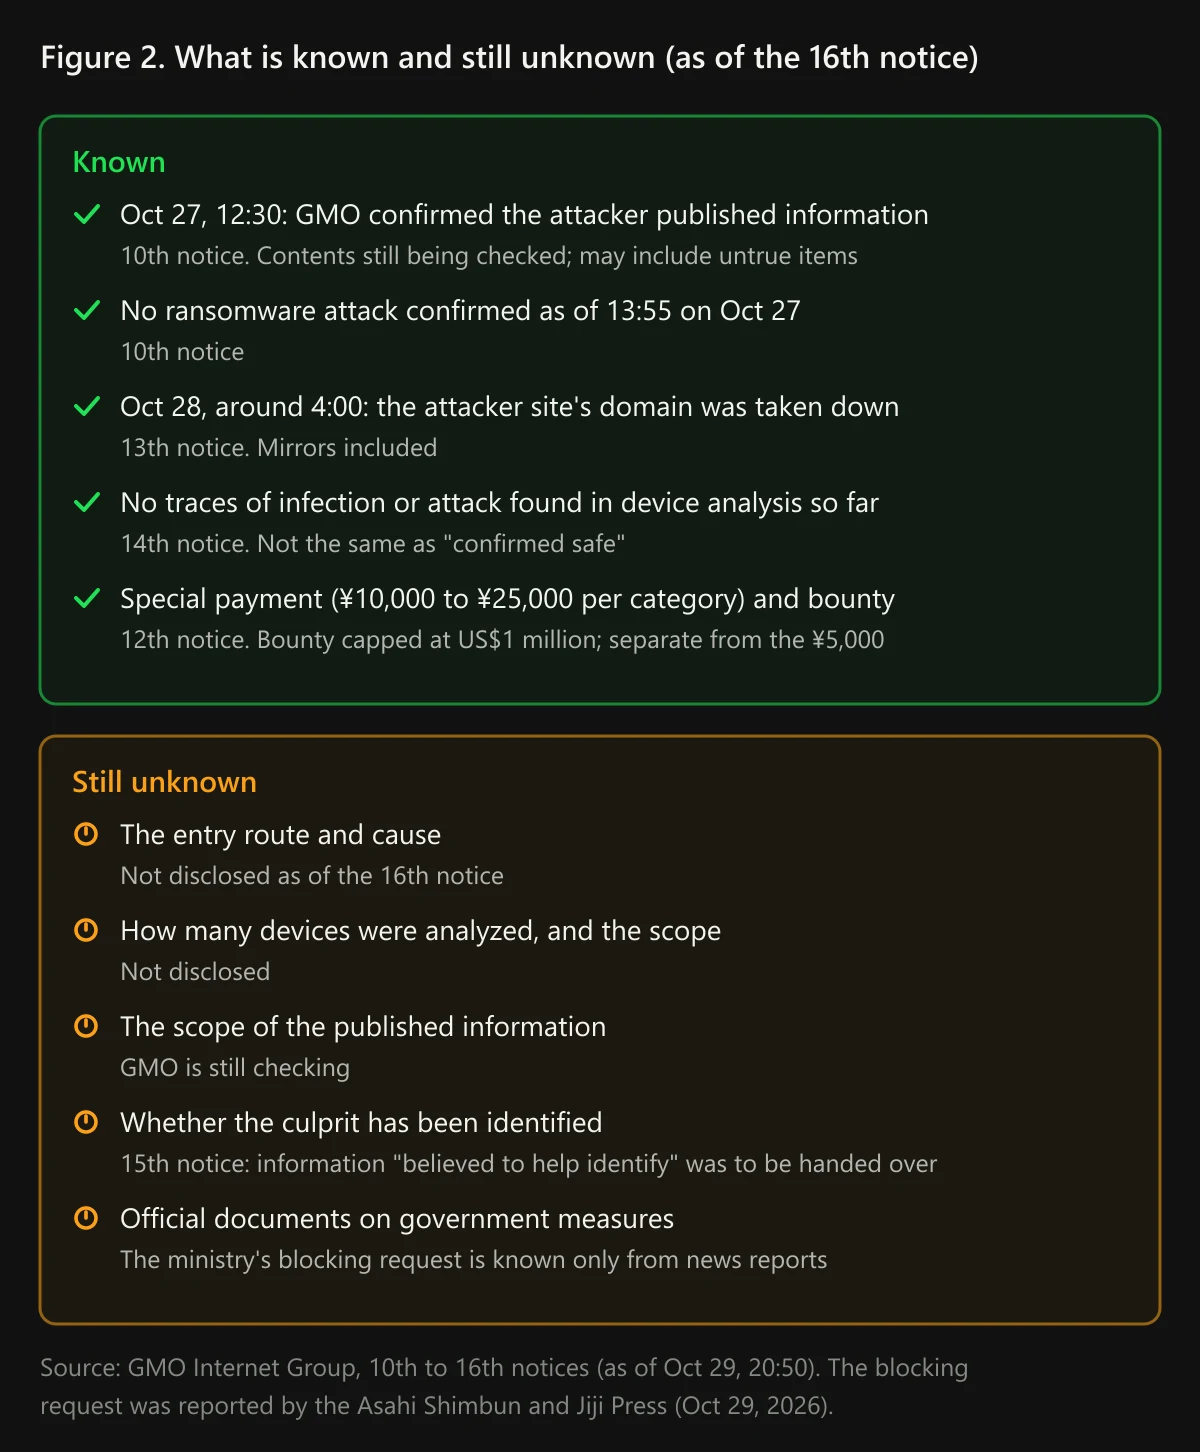
- What is still unknown
- Sources
The previous update covered up to the 9th notice (Oct 27, 11:59). Since then, GMO has published seven more, the 10th through the 16th, by October 29.
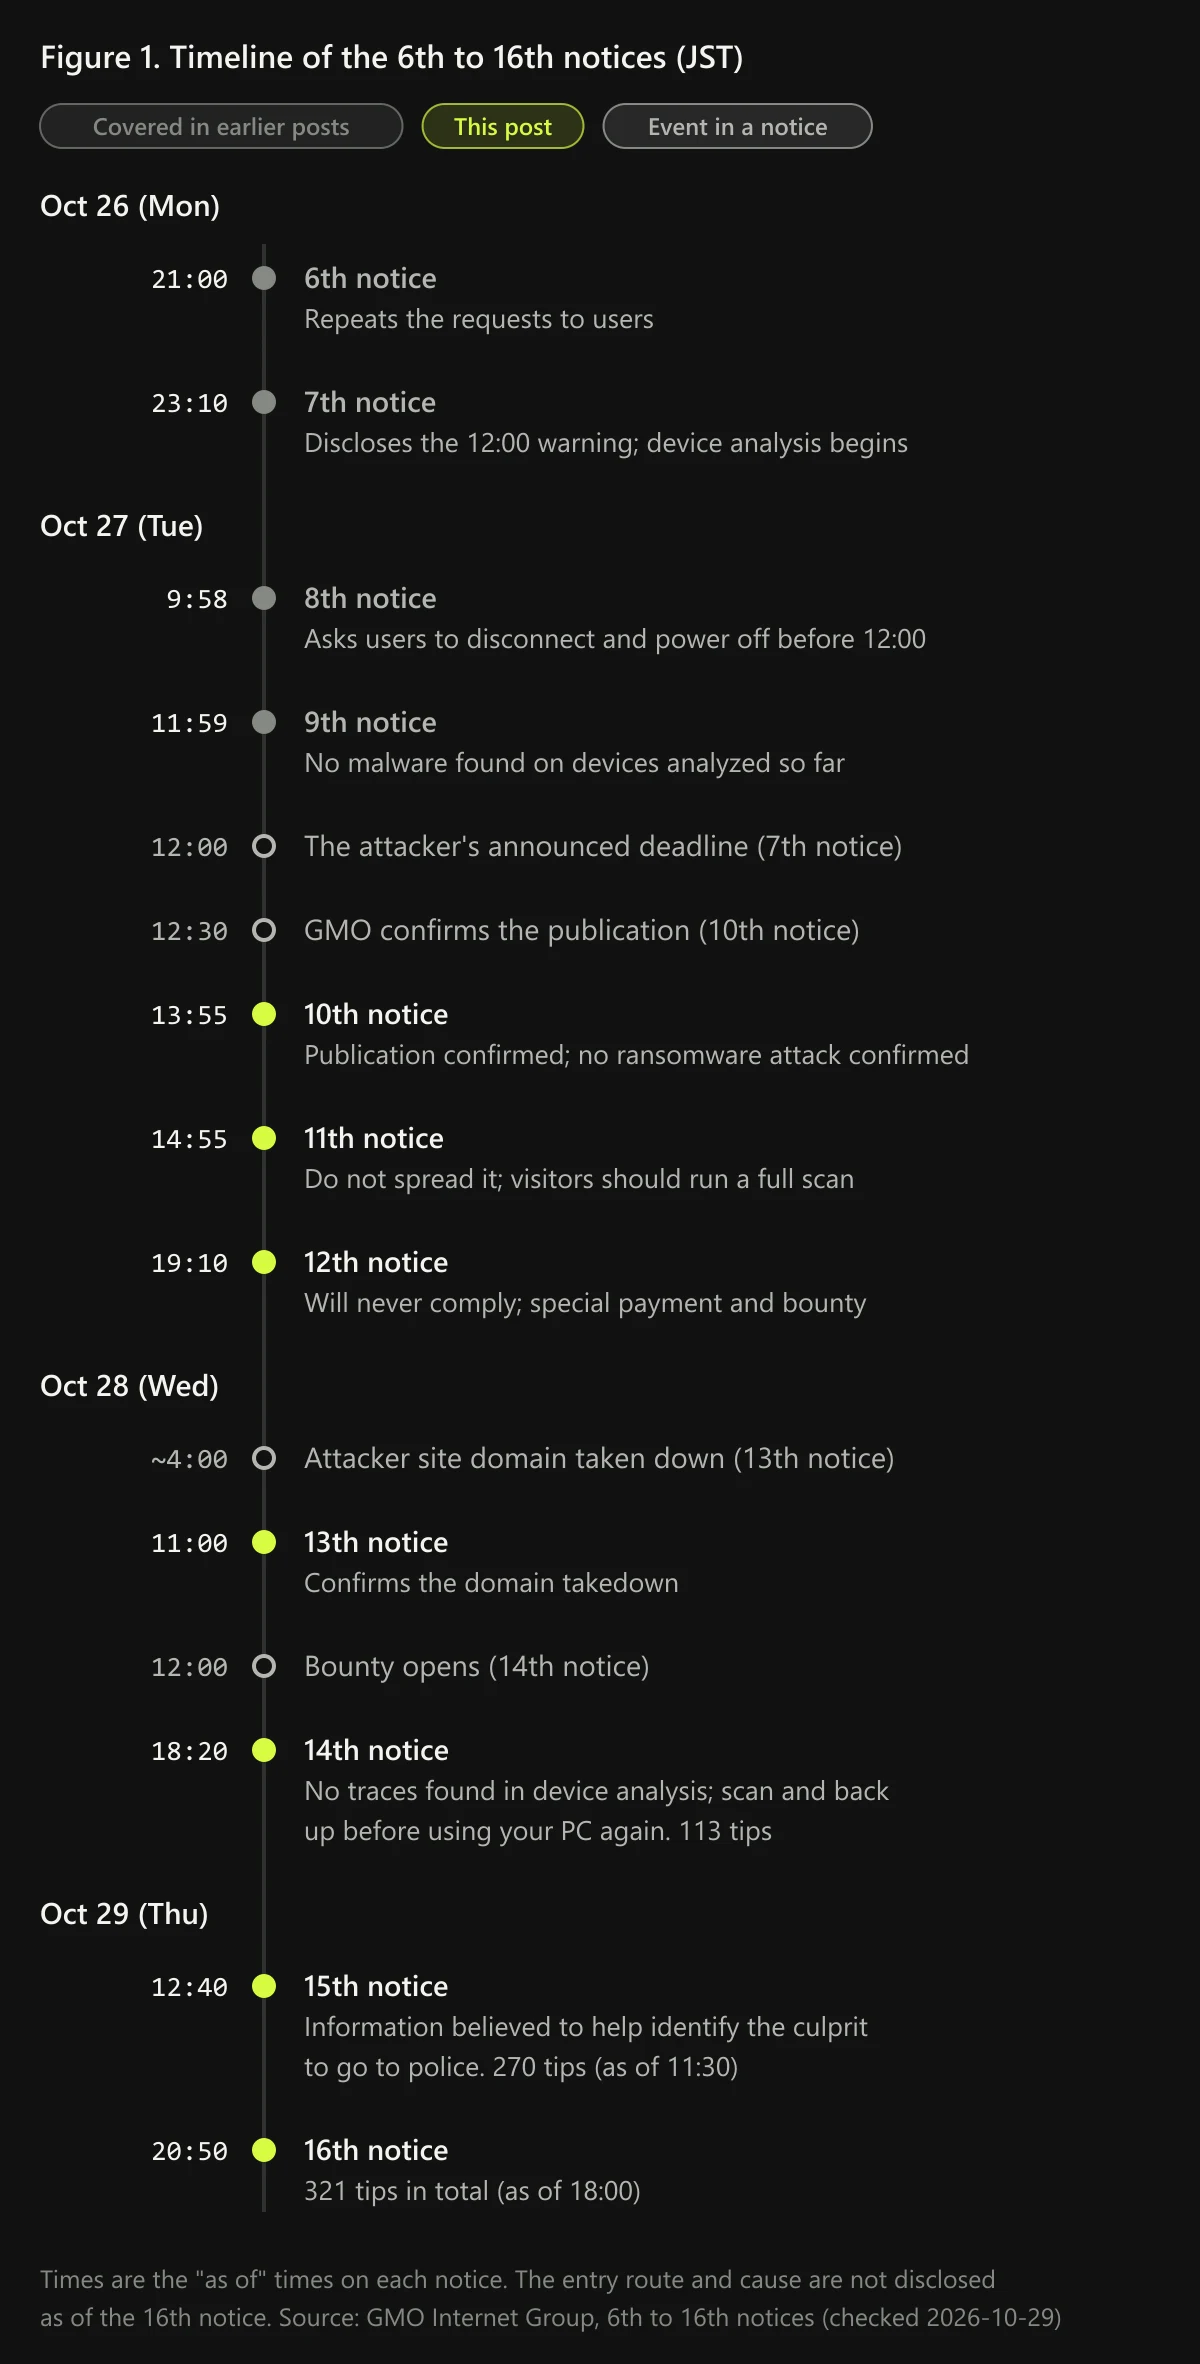
The biggest change is that questions the previous update left open now have answers. After the 12:00 deadline, GMO confirmed at 12:30 on October 27 that information had been published. As of 13:55 that day, no ransomware attack had been confirmed. The domain of the attacker’s site was taken down at around 4:00 on October 28.
On the other hand, GMO has not disclosed the entry route or the cause, as of the 16th notice. In a post of Oct 24 on its own site, the attacker claims the VPSs sat in one Active Directory environment with an admin-level account that worked on every server. GMO has not addressed this and we could not confirm it (details in article 1).
The seven notices at a glance
| Notice | As of (JST) | What is new |
|---|---|---|
| 10th | Oct 27, 13:55 | Publication of information by the apparent attacker confirmed at 12:30. No ransomware attack confirmed as of 13:55. GMO started considering a payment for people whose information was published |
| 11th | Oct 27, 14:55 | Asks people not to spread the information. Anyone who already visited the site should run a full scan |
| 12th | Oct 27, 19:10 | GMO will “never” comply with demands. Sets up a “GMO Special Goodwill Payment” and the “GMO Cybercrime Bounty” |
| 13th | Oct 28, 11:00 | Confirms that the domain of the attacker’s site, including mirrors, was taken down at around 4:00 on Oct 28 |
| 14th | Oct 28, 18:20 | Analysis of collected devices has found no traces of malware infection or ransomware attack so far. Scan and back up before using your PC again |
| 15th | Oct 29, 12:40 | GMO’s white-hacker team obtained information believed to help identify the culprit, to be handed to the police and others that day |
| 16th | Oct 29, 20:50 | 321 tips to the bounty in total as of 18:00 on Oct 29. Counts will be posted at 18:00 on weekdays (Monday to Friday, except holidays) |
After the 12:00 deadline (10th and 11th notices)
In the 10th notice, GMO said it confirmed at 12:30 on October 27 that the apparent attacker had published “what they claim is information about our company and our customers.” GMO is still checking the contents and says they “may include information that is not true.”
As for ransomware, GMO says no attack “had been confirmed as of 13:55 on October 27.”
GMO strongly asks people not to visit or spread anything that claims to be the published information. The 10th notice says the information of people who visit that site is captured by the attacker, and the 11th notice says GMO “has confirmed” this. Anyone who already visited is asked to run a full scan with antivirus software.
This post does not cover the published contents, because they could identify individuals.
The attacker’s site taken down (13th notice)
According to the 13th notice, GMO worked with the companies involved and confirmed that the domain of the attacker’s site, including mirror sites, was taken down at around 4:00 on Wednesday, October 28.
If a similar new site appears, GMO says it will move to take it down as soon as it is confirmed. It warns that it will record and preserve posts that spread the site, such as links, reposts and quote posts, report them to X and to the police, and take legal action against malicious ones.
Device analysis (14th notice)
On the devices collected from users, the 14th notice (as of Oct 28, 18:20) says:
- The investigation so far has found no traces of malware infection or ransomware attack
- Detailed investigation continues
As the previous update said, “not found” is different from “confirmed safe.” The number of devices analyzed and the scope of the analysis have not been disclosed, as of the 16th notice.
Special payment and bounty (12th notice)
The 12th notice adds two programs. They are separate from the earlier goodwill payment (a flat ¥5,000 from the 4th notice) and from compensation for losses from unauthorized trades.
The GMO Special Goodwill Payment goes to users whose information GMO has confirmed is in what the attacker published. The amount depends on the category of information published.
| Category of published information | Amount |
|---|---|
| Basic information such as name and contact details | ¥10,000 |
| Financial and authentication information such as trading account IDs and passwords | ¥15,000 |
| Highly private information such as sensitive personal information | ¥25,000 |
If several categories are published, the amounts are added up, with a cap of ¥3 million per publication. GMO will contact eligible users individually.
The GMO Cybercrime Bounty pays for information that helps identify the culprit or solve the case. The cap for the whole program is US$1 million in total (about ¥150 million at ¥150 per dollar, for reference). It opened at 12:00 on October 28. GMO reported 113 tips as of 18:00 on October 28, and 321 in total as of 18:00 on October 29.
This “US$1 million” is the cap on rewards for tipsters. It is not the same as the “US$1 million” shown on the attacker’s site, or the demand disclosed in the Oct 26 addendum to GMO’s CEO blog (US$50 million).
Toward identifying the culprit (15th notice)
In the 15th notice, GMO said its group’s white-hacker team had investigated on its own and obtained “information believed to help identify the culprit.” GMO said it would hand this to the police and others that day.
It does not say the culprit has been identified. What the information is has not been disclosed. GMO asks people not to try to identify or contact the culprit themselves.
What news reports say
The three items below come from news reports, not from GMO. We have not seen first-hand statements from the parties for any of them.
- The Ministry of Internal Affairs and Communications asked for blocking: On October 29, the Asahi Shimbun and Jiji Press reported that the ministry had asked telecom carriers, through industry groups, to block access to the site believed to be the attacker’s. The Asahi says the request was dated the 27th. Jiji says the carriers have not said whether they did it
- Tokyo police investigation: On October 29, FNN reported that the Tokyo Metropolitan Police Department has started investigating on suspicion of violating the Unauthorized Computer Access Act. The Asahi and Jiji articles above do not mention it (checked Oct 29)
- Reports of losses from FX firms: On October 27, Jiji Press reported that the financial services minister told a press conference that five FX firms had reported customer losses “believed to be related to GMO.” The Financial Services Agency has asked FX firms, through the Financial Futures Association of Japan, to strengthen their measures
In a search on October 29, 2026, we found no warning from a public body (IPA, JPCERT/CC, the National Police Agency, the National Cybersecurity Office, the Personal Information Protection Commission, or the FSA) that names this incident. JPCERT/CC has a warning about the recent wave of unauthorized access in Japan (JPCERT-AT-2026-0030), but it does not name this incident.
What users should do
These are the instructions in GMO’s 10th to 16th notices.
- Do not visit anything that claims to be the published information. Do not repost it, share it on social media, or share links to it (10th to 13th notices)
- If you already visited it, run a full scan with antivirus software (11th and 12th notices)
- If you powered off your PC, run a security scan and make a backup before you use it again (14th notice)
- Be careful with messages claiming to be from GMO. GMO will never ask for your password or authentication code. Do not answer messages asking for fees to “recover lost funds.” Do not open links or attachments in emails or SMS; check GMO’s official site instead (10th to 12th notices)
- If you find a new attacker site, or a site publishing personal information, report it through GMO’s form (https://www.onamae.com/abuse/), choosing the options for website content and inappropriate content. Do not try to identify or contact the culprit yourself (14th to 16th notices)
The support desk is the contact form (https://help.onamae.com/contact/) and phone 03-5456-2560 (24 hours, including weekends and holidays).
The advice in our earlier posts, such as changing passwords and checking your .rdp file, still stands. The steps are in post 3.
The entry route may stay unconfirmed
In its 2nd and 3rd notices, GMO wrote that it was “investigating the intrusion route and the scope of impact together with a security firm.” In the 4th notice it acknowledged that “a security problem exists in the system of this service,” but did not say what the problem was. In the text of the 5th to 16th notices, we found no passage where GMO itself explains the intrusion route (checked Oct 30).
The 8th to 10th notices say GMO will let users know if “newly confirmed facts or measures users should take” come up. That is a promise about facts and measures that affect users, not a promise to explain the route or the cause. The investigation could end without its results being published.
So the route the attacker claimed in its Oct 24 post (VPSs joined in one Active Directory environment, an admin-level account that worked on every server, credentials that could be pulled when a support engineer connected) may stay unconfirmed by GMO’s own notices. This article treats it as the attacker’s claim, not as fact.
Putting the attacker’s account in order
Here is the attacker’s account, laid out in the order it would have happened. From here on it is our own inference, not a confirmed fact.
- Entry. The attacker writes that when a support engineer connected to a user’s PC, the user could pull the credentials of an admin-level account. We read “user” here as the attacker having rented a VPS of their own.
- Moving sideways. The attacker claims those credentials worked on every VPS, and because the VPSs were joined in one Active Directory environment, one machine led to all of them.
- Into the user’s PC. The attacker claims they went from the VPS into the user’s PC through the drive sharing in the distributed
.rdpfile (article 2).
Two things make this order plausible.
- In the 4th notice GMO acknowledged that “a security problem exists in the system of this service,” and it stopped the servers of every plan. That is a response that suspects the whole environment, which does not fit a story of one compromised machine.
- On Windows, once an administrator logs on, material from their credentials stays in memory and can be pulled out by anyone with administrative rights (MITRE ATT&CK T1003.001). That credentials could be left on a VPS a support engineer connected to is technically possible.
There are also things we cannot confirm.
- We do not know that this was really the way in. A vulnerability or leaked credentials could have been another entrance.
- The
.rdpin step 3 is about how an intruder spreads from a VPS to a user’s PC. It does not explain how the attacker first got into GMO’s VPS network. - “Since 2019,” “over 7 years,” and “intentional negligence” are the attacker’s words, and there is no way to check them.
You do not need to wait for the route to be known. What users should do is the same whichever route it was. If GMO publishes the route or the cause, we will correct this article.
What is still unknown
- The entry route and the cause. Not disclosed as of the 16th notice, and it is unclear whether they will be (section above)
- How many devices have been analyzed, and the scope of the analysis
- The scope and contents of the published information. GMO says it is still checking and that it may include things that are not true
- Whether the information in the 15th notice led to identifying the culprit
- Government measures. The ministry’s request is known only from news reports; we have not seen an official document. We also have not confirmed whether active cyber defense was invoked
- Whether the distributed
.rdpfiles had drive sharing turned on from the start. GMO’s notices do not address this
Sources
- GMO インターネットグループ 第 10 報(2026-10-27 13:55 時点)group.gmo/info/alert/2026102703/
- 同 第 11 報(2026-10-27 14:55 時点)group.gmo/info/alert/2026102704/
- 同 第 12 報(2026-10-27 19:10 時点)group.gmo/info/alert/2026102705/
- 同 第 13 報(2026-10-28 11:00 時点)group.gmo/info/alert/20261028/
- 同 第 14 報(2026-10-28 18:20 時点)group.gmo/info/alert/2026102802/
- 同 第 15 報(2026-10-29 12:40 時点)group.gmo/info/alert/20261029/
- 同 第 16 報(2026-10-29 20:50 時点)group.gmo/info/alert/2026102902/
- GMO インターネットグループ 代表ブログ(2026-10-26 追記。要求額)www.kumagai.com/?eid=19600
- 朝日新聞「GMO不正アクセスの脅迫サイト 総務省が通信会社に強制遮断を要請」(2026-10-29)www.asahi.com/articles/ASVBX4G9KVBXULFA031M.html
- 時事通信「『攻撃者』サイトの強制遮断要請 GMO不正アクセスで―政府」(2026-10-29)www.jiji.com/jc/article?k=2026102900531&g=eco
- 時事通信「片山金融相、FX業者5社に被害 GMO不正アクセス関連で」(2026-10-27)www.jiji.com/jc/article?k=2026102700409&g=eco
- FNN プライムオンライン(2026-10-29)www.fnn.jp/articles/-/1141889
- JPCERT/CC「直近で相次いでいる国内組織における不正アクセスに関する注意喚起」(JPCERT-AT-2026-0030、2026-10-23 更新)www.jpcert.or.jp/at/2026/at260030.html
Checked on 2026-10-29